Key Takeaways
An AI agent is an autonomous program that observes its environment, reasons about a goal and acts through connected tools, without waiting for a human instruction at every step. Unlike a language model that mainly produces text, an agent produces operational outcomes: it can update, trigger, classify or route information.
- An AI agent combines four modules: reasoning, memory, planning and action. It can act on your systems to pursue a goal without requiring human validation at every step.
- Its role is to take on complex, repetitive tasks that teams no longer have time to handle, from process automation and content generation to data analysis.
- It operates in a loop: profiling the context, consulting its memory, breaking the task down into a plan, then executing actions through its tools.
- There are two main families: single agents and multi-agent systems, with three main architectures: hierarchical, peer-to-peer and functional-role based.
- Deployment follows five steps: define a measurable objective, structure the memory, standardise connections, calibrate access rights, then test on real cases before production.
- Through its DMS and MCP connector, Efalia provides the structured document base and source-level permission propagation that agents need to operate reliably.
What Is an AI Agent?
An artificial intelligence agent (also called an intelligent agent) is a computational entity situated in an environment, capable of observing it, deliberating through a reasoning engine, and acting autonomously towards a defined goal. It combines decision-making capabilities, natural language processing and tool integration to complete tasks in context (Cheng et al., 2026; Li et al., 2024).
It is not a model. The literature is categorical: “an autonomous AI agent cannot be reduced to a foundation model”.
The Four Defining Properties of an AI Agent
(Cheng et al., 2026; Botti, 2025; Molinari & Ciravegna, 2026)
These four properties describe how an agent works: it can operate over a long sequence, respond to changes, take initiative to achieve a goal and cooperate with other actors. The table below explains each property in simple terms and provides a concrete example.
Combined, these properties produce continuous autonomy and adaptation: when faced with the unexpected, the agent re-evaluates and adjusts its plan. This autonomous decision-making distinguishes it from a conventional program, and makes its supervision essential.
How AI Agents Differ from Bots and Assistants
A bot executes. An assistant advises. An AI agent decides and acts. The deciding criterion: can it modify something in your systems without being asked to at every step?
What Is the Role of an AI Agent?
AI agents are being deployed across five major areas:
- Process automation (augmented RPA) : the agent chains tasks across systems without a rigid script.
- Analytics and monitoring : it collects, cross-checks and summarises data continuously.
- Content generation and management : it drafts, classifies and updates documents according to business rules.
- Augmented customer service : it handles routine requests and escalates complex cases.
- Proactive cybersecurity : it detects anomalies and triggers responses without waiting for human intervention.
In the table below, maturity refers to the level of actual business deployment today: high means a common and industrialised use; medium means that the use case is still being actively tested; low means that it remains an emerging use case.
What AI Agents Look Like in Production Today
An AI agent’s role is not to replace judgement: it absorbs the preparation work that precedes it. The real gain: automating complex but repetitive tasks that consume expert time without drawing on expert insight.
How Does an AI Agent Work?
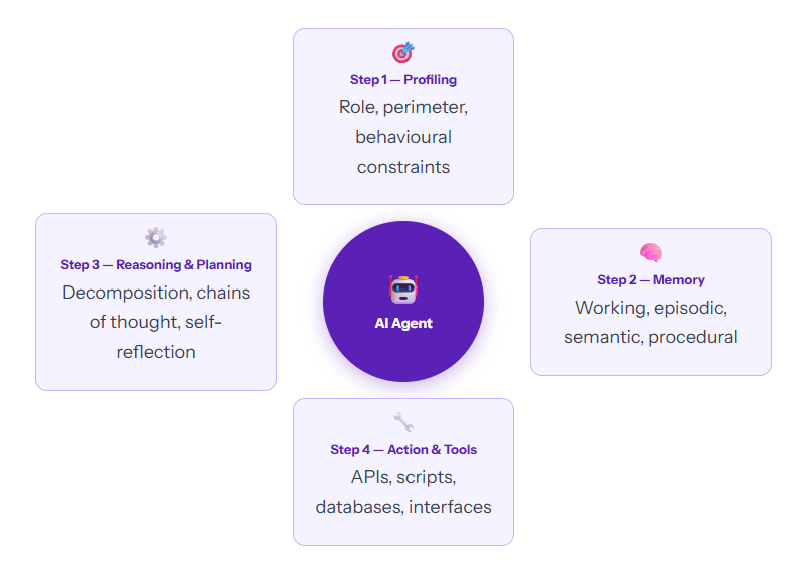
An AI agent operates through an organised loop: it first defines its role and objective, then retrieves the information it needs, builds an action plan and finally uses the appropriate tools to achieve a concrete result.
Four interconnected modules.
Step 1: Profiling: defining its role and objective
First, the agent establishes its profile: it is given a business role, an objective, an operating scope and behavioural constraints. This defines the framework within which it must make decisions. An agent responsible for compliance checks will therefore reason differently from one dedicated to sales support, even if both use the same language model.
Step 2: Memory: retrieving the information it needs
Once its role has been defined, the agent consults its memory to understand the context and retrieve the information relevant to its task. This memory includes the current state of the task, previous experiences, available knowledge and business rules. RAG plays a key role here by allowing the agent to search a document base instead of relying solely on the model's parameters. In practice, the agent does not rely only on what it learned during training: it retrieves the relevant documents, reads them in context and uses them to build its response or decide what action to take.
Remember this: an agent's long-term memory is your document base.
Your contracts, procedures and files. This is where your AI-enabled DMS becomes the agent's infrastructure rather than a simple storage space.
Step 3: Reasoning and planning: deciding how to act
Based on its objective and the information it has retrieved, the agent builds an action plan. It can break down a complex task into several steps, compare different approaches and reconsider its reasoning when the first one does not work. This planning can rely on chains, trees or graphs of thought, external symbolic planning, or self-reflection loops such as ReAct and Reflexion.
Step 4: Action and tools: executing the plan
Finally, the agent takes action. It calls APIs, queries databases, runs scripts or interacts with business applications. It can also retrieve information from external systems. This final step turns reasoning into a concrete result: without access to tools, an agent remains capable of producing text, but unable to act in the real world.
This formula does not require any calculation from the reader: it simply summarises the five building blocks an agent needs to operate. It needs a reasoning engine, a mission to accomplish, memory, tools to act and the ability to correct itself.
Cheng et al. (2026) formalise the agent as a quintuple: V = (L, O, M, A, R)
Remove any single element: you no longer have an agent, you have a chatbot.
What Are the Different Types of AI Agents?
Single-Agent Systems
A single-agent system handles an entire task within one decision loop. This architecture is well suited to focused tasks because it limits communication between components and remains relatively simple to deploy. It reaches its limits, however, when the task becomes lengthy or complex, or requires several distinct areas of expertise.
Multi-Agent Systems
A multi-agent system distributes a task among several specialised agents. Each agent can handle a specific function: analysing, writing, reviewing or orchestrating, and then pass its output to the others. This organisation makes it possible to handle more complex tasks, but it requires more coordination and control.
Multi-agent systems can then be organised according to three main architectures:
The Five Levels of Autonomy
How to Create and Deploy an AI Agent?
Step 1: Define a Verifiable Objective
Write an objective a third party could verify: ❌ “Automate invoice management” vs ✅ “Extract the number, pre-tax amount, due date and supplier from every PDF invoice, then flag any duplicate from the past 90 days”.
In other words, the challenge is not only to write a clear instruction: it is to define an outcome that leaves no ambiguity about what must be done and how success will be checked.
Step 2: Structure Memory Before Intelligence
Connect your agent to a disorganised base, and the result won’t be approximate. It will be wrong, with confidence.
.ctaage-w{font-family:inherit;background:#f5f3ff;border:1.5px solid #c4b5fd;border-radius:12px;padding:24px 28px;display:flex;align-items:center;justify-content:space-between;flex-wrap:wrap;gap:16px}.ctaage-txt h3{font-size:18px;font-weight:700;color:#111827;margin:0 0 4px}.ctaage-txt p{font-size:14px;color:#374151;margin:0}.ctaage-btn{display:inline-flex;align-items:center;gap:8px;background:#5b21b6;color:#fff;font-size:15px;font-weight:600;padding:12px 24px;border-radius:8px;text-decoration:none;white-space:nowrap}
Want to test Efalia’s AI DMS?
Discover how to structure your document memory before deploying an agent.
Request a Free Demo →
Step 3: Standardise Connections via Open Protocols
In practical terms, MCP acts as a common interface: it allows an agent to discover and use different tools through standardised rules, without requiring a separate custom connection for every application.
Step 4: Choose a Platform and Calibrate Permissions
Efalia integrates with DUST, Microsoft Copilot Studio, Google Agentspace and IBM watsonx Orchestrate via MCP. User permissions defined in the DMS are propagated to the agent.
Step 5: Test the Agent Before Trusting It
One lesson follows: do not automatically choose the most intelligent model. GAIA-2 shows inverse scaling over time: models that reason for longer can fail when a time limit applies. They may be more capable, but too late. Choose by task: speed for extraction and sorting, depth for contract analysis. In other words, the best answer is not always the one produced after the longest reasoning process: it also needs to arrive within the time available for the task.
Risks and Key Considerations
The Risk Shift
An agent hallucination “translates directly into destructive, persistent and irreversible material actions in databases”. This is an integrity problem for your information system. Human-in-the-loop oversight, meaning that a person reviews or approves certain actions, data privacy and ethical considerations are essential when an agent can access enterprise systems or modify data.
At Efalia, this risk management starts with the document architecture: agents rely on a structured DMS, permissions propagated from the source and controlled connections to business tools. The MCP connector then helps govern their actions and limit their operating scope. The agent therefore does not receive unrestricted access to information: it operates within the document, functional and security framework defined by your organisation.
The Five Families of Hallucinations
Agent drift (Xu et al., 2026): over a long trajectory, an initial imprecision can propagate and turn subsequent tools into “confused agents executing aberrant but syntactically valid actions”. In plain terms, a small error at the beginning of a multi-step task can be carried forward into the next steps. Each tool call may appear valid, while the final result gradually moves further away from the original objective.
Security: AI Is Not Yet Particularly Safe
Blocking Alone Is Not Enough
A useful safeguard explains why the action is refused, proposes an alternative, and escalates to a human when no path fits.
The Sovereignty Question
Open models reach 60–95% of GPT-4 performance on targeted domains. Our article on how AI improves document management in the enterprise.
Conclusion
👉 Discover our AI DMS platform at efalia.com/start-ia.
Frequently Asked Questions
What is the difference between an AI agent and an AI assistant?
An AI assistant responds to your prompts. An AI agent pursues a goal and acts on its own initiative: chaining steps, calling tools and modifying data without validation at every move.
What is the difference between an AI agent and an LLM?
The LLM produces text; the agent uses it as a reasoning engine. Around it: role profile, structured memory, planning, tools. V = (L, O, M, A, R).
What are the most widespread AI agent examples?
Code agents, customer support agents, document agents.
Can an AI agent work without structured documents?
Technically yes, but poorly controlled documents directly bias the agent’s reasoning (Knowledge Poisoning, He et al., 2025). In other words, if documents are inaccurate, contradictory or deliberately manipulated, the agent may treat them as reliable and build an incorrect line of reasoning from that information.
What autonomy level for a first project?
L2 or L3: consultant agent with human validation, or collaborative agent with sampling-based supervision.
Do you need technical skills to create an AI agent?
No. The key skill: formulating a semantically verifiable objective.
How do you know if your agent is working correctly?
Do not ask an AI to evaluate it: Froger et al. (2026) measured an accuracy of 0.52 for this method, compared with 0.99 when directly checking the changes produced. Audit the actual changes in your databases, files and tickets. Not the apparent quality of the answers.
GDPR compatibility?
Open models reach 60–95% of proprietary performance without data leaving your infrastructure.
Sources
Literature review: 2026 State of the Art on Artificial Intelligence Agents, 17 September 2026. Corpus: 220 records → 148 after deduplication → 21 retained, including 15 full-text studies analyzed.
- Botti, V. (2025). Agentic AI and Multiagentic: Are We Reinventing the Wheel? arXiv:2506.01463
- Cheng, Y., et al. (2026). Exploring LLM-Based Intelligent Agents. WIREs DMKD. doi:10.1002/widm.70111
- Chowa, S. S., et al. (2026). From language to action. Artificial Intelligence Review. doi:10.1007/s10462-025-11471-9
- Dantas, P., et al. (2026). Toward Safe LLM Agents. arXiv:2608.14590
- Froger, R., Andrews, P., & Bettini, M. (2026). GAIA-2. ICLR 2026
- He, F., et al. (2025). The Emerged Security and Privacy of LLM Agent. ACM CSUR. doi:10.1145/3773080
- Li, X., et al. (2024). A survey on LLM-based multi-agent systems. Vicinagearth. doi:10.1007/s44336-024-00009-2
- Lin, X., et al. (2025). LLM-Based Agents Suffer from Hallucinations. arXiv:2509.18970
- Mohamed, N., et al. (2026). A Systematic Survey of LLM-Based Agentic AI Frameworks. JSSA. doi:10.66279/y29vex64
- Molinari, G., & Ciravegna, F. (2026). Towards Pervasive Distributed Agentic Generative AI. ACM CSUR. doi:10.1145/3821566
- Sarkar, A., & Sarkar, S. (2025). Survey of LLM Agent Communication with MCP. arXiv:2506.05364
- Su, H., et al. (2026). Autonomy-Induced Security Risks in Large Model-Based Agents. IEEE TDSC. doi:10.1109/TDSC.2026.11498611
- Weng, S., et al. (2026). ARGUS. arXiv:2605.03378
- Xu, H., et al. (2026). The Evolution of Tool Use in LLM Agents. arXiv:2603.22862
- Yang, Y., et al. (2026). AgentNet. NeurIPS